Montana Consumer Data Privacy Act (MCDPA), the data privacy law of Montana, gives residents greater control over how businesses collect, use and share their personal data.
The law took effect on 1 October 2024 and was amended by Senate Bill 297 (SB 297), effective 1 October 2025. The amendment expanded the law's coverage, introduced stronger protections for minors and updated privacy notice and enforcement requirements.
This guide explains who must comply with the MCDPA, what rights consumers have and the steps businesses should take to meet its requirements.
Effective date: October 1, 2024; amended by SB 297, effective 1 October 2025
What is the Montana Consumer Data Privacy Act (MCDPA)?
Similar to other US privacy laws, MCDPA also guarantees digital privacy to individuals. Along with conferring rights to consumers, it also lists the data processing requirements that businesses should follow.
The MCDPA legislation designates the Attorney General as its enforcement agency. Non-compliance fines can reach up to $7500 per violation.
MCDPA expressly prohibits the use of dark patterns to obtain consent from consumers. Since 1 October 2025, the law also protects consumers under 18 whom a business knows, or wilfully disregards, are minors. Businesses need the minor’s consent, or a parent’s or guardian’s consent for children under 13, before processing their data for targeted advertising, sale or significant profiling. The 60-day cure period no longer applies, so the Attorney General can take action without giving businesses time to fix a violation first.

Jump to
Tips for MCDPA ComplianceWho does the MCDPA apply to?
The applicability of Montana’s data privacy law is not based on a monetary threshold like CCPA.
MCDPA applies to for-profit businesses based in Montana or businesses elsewhere that target the residents of Montana and:
- Controls/ processes the personal data of at least 25,000 consumers except to complete a payment transaction; or
- Controls/ processes personal data of at least 15,000 consumers and gains 25% or more of its gross revenue from the sale of personal data.
Who is a consumer under Montana privacy law?
A consumer is a resident of Montana who does not act in a commercial or employment context.
In addition, any employee, director, owner, officer, or contractor of a company, partnership, sole proprietorship, nonprofit, or government agency is not a consumer if the communication/transactions with the controller/business occur within the context of their role.
What are the exemptions to MCDPA?
The MCDPA exempts certain organisations and categories of information. Organisations that may qualify for an exemption include:
- Government bodies and public agencies
- Institutions of higher education
- Certain banks, credit unions and their qualifying affiliates or subsidiaries
- Certain insurers, insurance producers and related entities
- HIPAA-covered entities and business associates
- Nonprofit organisations established to detect and prevent insurance fraud
- Registered national securities associations
The law also exempts certain types of information, including personal data processed in accordance with the Gramm-Leach-Bliley Act (GLBA), protected health information under HIPAA and other information covered by specified federal laws.
Most nonprofit organisations are no longer automatically exempt from the MCDPA.
What does personal data mean under MCDPA?
Personal data is any information that can potentially identify an individual.
The act defines personal data as any information that is linked or reasonably linkable to an identified or identifiable individual. Phone numbers, email addresses, IP addresses, cookie IDs, etc might come under the category of personal data.
De-identified data and publicly available information are not personal data under MCDPA.
What is de-identified data?
De-identified data is information that cannot reasonably be linked to an identifiable individual or a device associated with them. To qualify, controllers must take reasonable steps to prevent identification, publicly commit not to re-identify the data and require recipients to follow the same safeguards through contracts.
What is publicly available information?
Publicly available information includes information lawfully available through government records or widely distributed media. It also includes information that a controller reasonably believes a consumer has lawfully made available to the public.
What is sensitive data under MCDPA?
Most privacy laws extend enhanced protection to sensitive data, therefore businesses must be cautious while processing it. Let us look at the types of data that are included as sensitive data under Montana’s privacy act.
Sensitive data under MCDPA includes:
- Any data that reveals a person’s
- racial/ethnic origin
- religious beliefs
- mental/physical health conditions or diagnosis
- sexual life
- Sexual orientation
- citizenship/immigration status
- Processing biometric/genetic data to identify an individual
- Personal data of a child below 13 years of age if the business is aware of the age (Known child)
- Precise geolocation data
What are the obligations/limitations of businesses under MCDPA?
Let’s look at the obligations/limitations of businesses under the Act.
Data minimization
Do not collect more personal data than what is reasonable or adequate for the purpose for which it was obtained from consumers. Unnecessary collection of personal data is a potential liability. Therefore, stick to the data minimization principle.
Purpose limitation
Just like data minimization, purpose limitation is also a significant duty of businesses. Always limit the processing of personal data to what is required for the specific purpose disclosed to the consumers. Remember, transparency is the key. Do not process additional personal data without obtaining affirmative consent from the consumers.
Security safeguards
When you are involved in the processing of personal data you are inherently under an obligation to implement reasonable security measures to prevent any unauthorized access or violations regarding the data collected. Therefore establish proportional technical, administrative, and physical data security safeguards to protect the confidentiality of the data handled.
Sensitive data
Do not process sensitive data without obtaining consent from the consumer. To process the sensitive data of a child who is known to be under 13 years old, obtain verifiable consent from parents/legal guardians. For this purpose, be in confirmation with the Children’s Online Privacy Protection Act.
Non-discrimination
Do not discriminate among the consumers based on the exercise of their rights. This means that businesses cannot deny goods/services, reduce the quality of the products/services offered, or increase their prices.
The following acts are not discrimination under the act:
- Denying a product/service if the personal data required for that purpose is not collected/maintained by the business.
- Varying the price, quality, selection, rate, and level of goods/services depending on the opt-outs made by the consumer.
- Varying the price, quality, selection, rate, and level of goods/services based on their participation in loyalty, discount, rewards, or club card programs and premium versions offered.
Also, adhere to the federal and state laws that prohibit unlawful discrimination.
Consent
Controllers must obtain consent before processing sensitive personal data.
Additional consent requirements apply when a controller knows, or wilfully disregards, that a consumer is under 18. These requirements cover targeted advertising, the sale of personal data, certain profiling activities and other processing or design practices restricted by the law. For children under 13, consent must come from a parent or legal guardian.
Protection of minors
SB 297 introduced additional privacy protections for consumers under 18.
Controllers that know or wilfully disregard that a consumer is a minor must use reasonable care to avoid exposing them to a heightened risk of harm through online services, products or features.
The law also requires consent before controllers can:
- Use a minor's personal data for targeted advertising or sale.
- Use a minor's personal data for profiling that supports decisions with legal or similarly significant effects.
- Process their data for incompatible purposes or retain it longer than reasonably necessary.
- Use design features intended to significantly increase or extend a minor's engagement with an online service.
- Collect precise geolocation data, subject to the law's specific conditions.
For children under 13, parental or guardian consent is required.
Controllers must also consider safeguards for direct messaging and conduct data protection assessments where an online service presents a heightened risk of harm to minors.
These obligations can apply even when a business does not meet the MCDPA's general data-processing thresholds.
Consent withdrawal
Provide the consumers with an easy method to withdraw their consent. Once a consumer revokes consent, Stop processing his personal data within 45 days.
Opt-out mechanisms
Businesses must reveal whether they will sell the personal data or use it for targeted advertising. Provide methods to opt out of sales, targeted advertising, and profiling. Recognize verifiable opt-out signals from authorized agents including the global opt-out mechanisms.
Privacy notice
Provide an accessible privacy notice to your consumers. It should be legible and meaningful. We will discuss the detailed privacy policy requirements subsequently.
Response plan
Craft a handy response plan for your business. Do not take more than 45 days to respond to and deliver the consumer request. If necessary, it can be extended to 90 days.
Notify the declinal of consumer requests, if any within 45 days.
Provide the method to appeal conspicuously and respond to appeals within 60 days. Also, mention how they can contact the attorney general in the event of denial of appeal.
Businesses are required to deliver the request for free once a year if it can be given without much hassles.
Contractual relationship
The law requires processors to abide by the directions of controllers. Processors are those who process personal data on behalf of controllers like businesses. Therefore, have a contractual relationship with data processors.
Determine the rights and obligations of each party, duration of the processing, types of data involved, nature and purpose of processing, etc in the contract. Also, ensure the processor’s compliance with the law, and require them to maintain the confidentiality and integrity of the data.
Data protection assessments
Regularly conduct assessments regarding the processing of data that poses a high risk like sensitive data, and personal data used for targeted advertising, sale, and profiling.
Data protection assessments must be documented and kept confidential. SB 297 also introduced assessment requirements for online services, products or features that pose a heightened risk of harm to minors.
Data breach notifications
The rules under computer security breach require businesses to give notification regarding breaches to consumers without undue delay. The Attorney general should also be notified of the breach.
What are the rights of consumers under MCDPA?
Like other US privacy acts, MCDPA also grants consumers certain rights over their data:
Right to confirm
Consumers have the right to confirm whether businesses are processing their data. They can also request to access such personal data, except for anything that reveals a trade secret.
Right to correct
Consumers can request businesses to correct any inaccurate information maintained by the businesses.
Right to delete
Consumers can request businesses to delete any personal data that is being processed by them. This includes the personal data provided by the consumers and those obtained from other sources.
Right to portability
If any consumer wishes to obtain a copy of their personal data maintained by businesses, they can request the same. They also have the right to receive the copy in a portable and readable format. This enables them to transfer the data conveniently.
Right to opt-out
Consumers can opt out of targeted advertising, sale of their personal data, and profiling at any time. They can also delegate this right to an authorized agent using technology including global opt-out mechanisms.
Consent Requirements under MCDPA
Consent is an important basis for processing personal data. Therefore, it is significant to understand what constitutes a valid consent.
What constitutes a valid consent?
- It should be an affirmative action and not given passively.
- Given freely and without any coercive efforts from businesses.
- Informed of what they are consenting to
- Specifically given
- Unambigously agree to the processing.
The following are not consent:
- Acceptance of general terms flooded with information instead of the specific purpose for which the consent is required.
- Hovering over, muting, pausing, or closing a given piece of content.
- The agreement was obtained using dark patterns.
Manage cookie consent without any hassle
Add a cookie consent banner and manage cookie consent to comply with Montana privacy law
Try for free- 14-day free trial
- Cancel anytime
Privacy notice requirements under MCDPA
A privacy notice informs consumers about the data handling practices of your business. The law requires controllers to provide a well-drafted privacy notice to the consumers.
Controllers must provide a clear and accessible privacy notice that includes:
- Categories of personal data collected and processed
- Purposes for processing personal data
- Categories of personal data sold or shared with third parties
- Categories of third parties receiving personal data
- An active email address or another way to contact the controller
- A plain-language explanation of consumer privacy rights and how to exercise them
- Instructions for appealing a denied consumer request
- The date the privacy notice was last updated
Controllers must also:
- Make the notice available in every language in which the relevant product or service is offered.
- Ensure it is reasonably accessible to people with disabilities.
- Provide a conspicuous link on their website homepage or relevant app page, with an additional link in the app where required.
- Offer a clear opt-out method outside the privacy notice if they sell personal data or use it for targeted advertising.
- Notify affected consumers of material changes to their privacy notice or practices and provide a reasonable opportunity to withdraw consent where required.
Businesses do not need a separate Montana-specific privacy notice if their existing privacy policy meets these requirements.
What is the penalty for violating MCDPA?
The Attorney General enforces the MCDPA. Since the SB 297 amendment, businesses that break the law can be fined up to $7,500 per violation. The Attorney General can also go to court to stop the violation and recover legal and investigation costs. There is no longer a 60-day cure period. The AG can act as soon as there is reason to believe a business has broken the law, without giving it time to fix the problem first.
Montana privacy law does not provide a private right of action, meaning, consumers cannot sue businesses under the MCDPA. Only the Attorney General can take action.
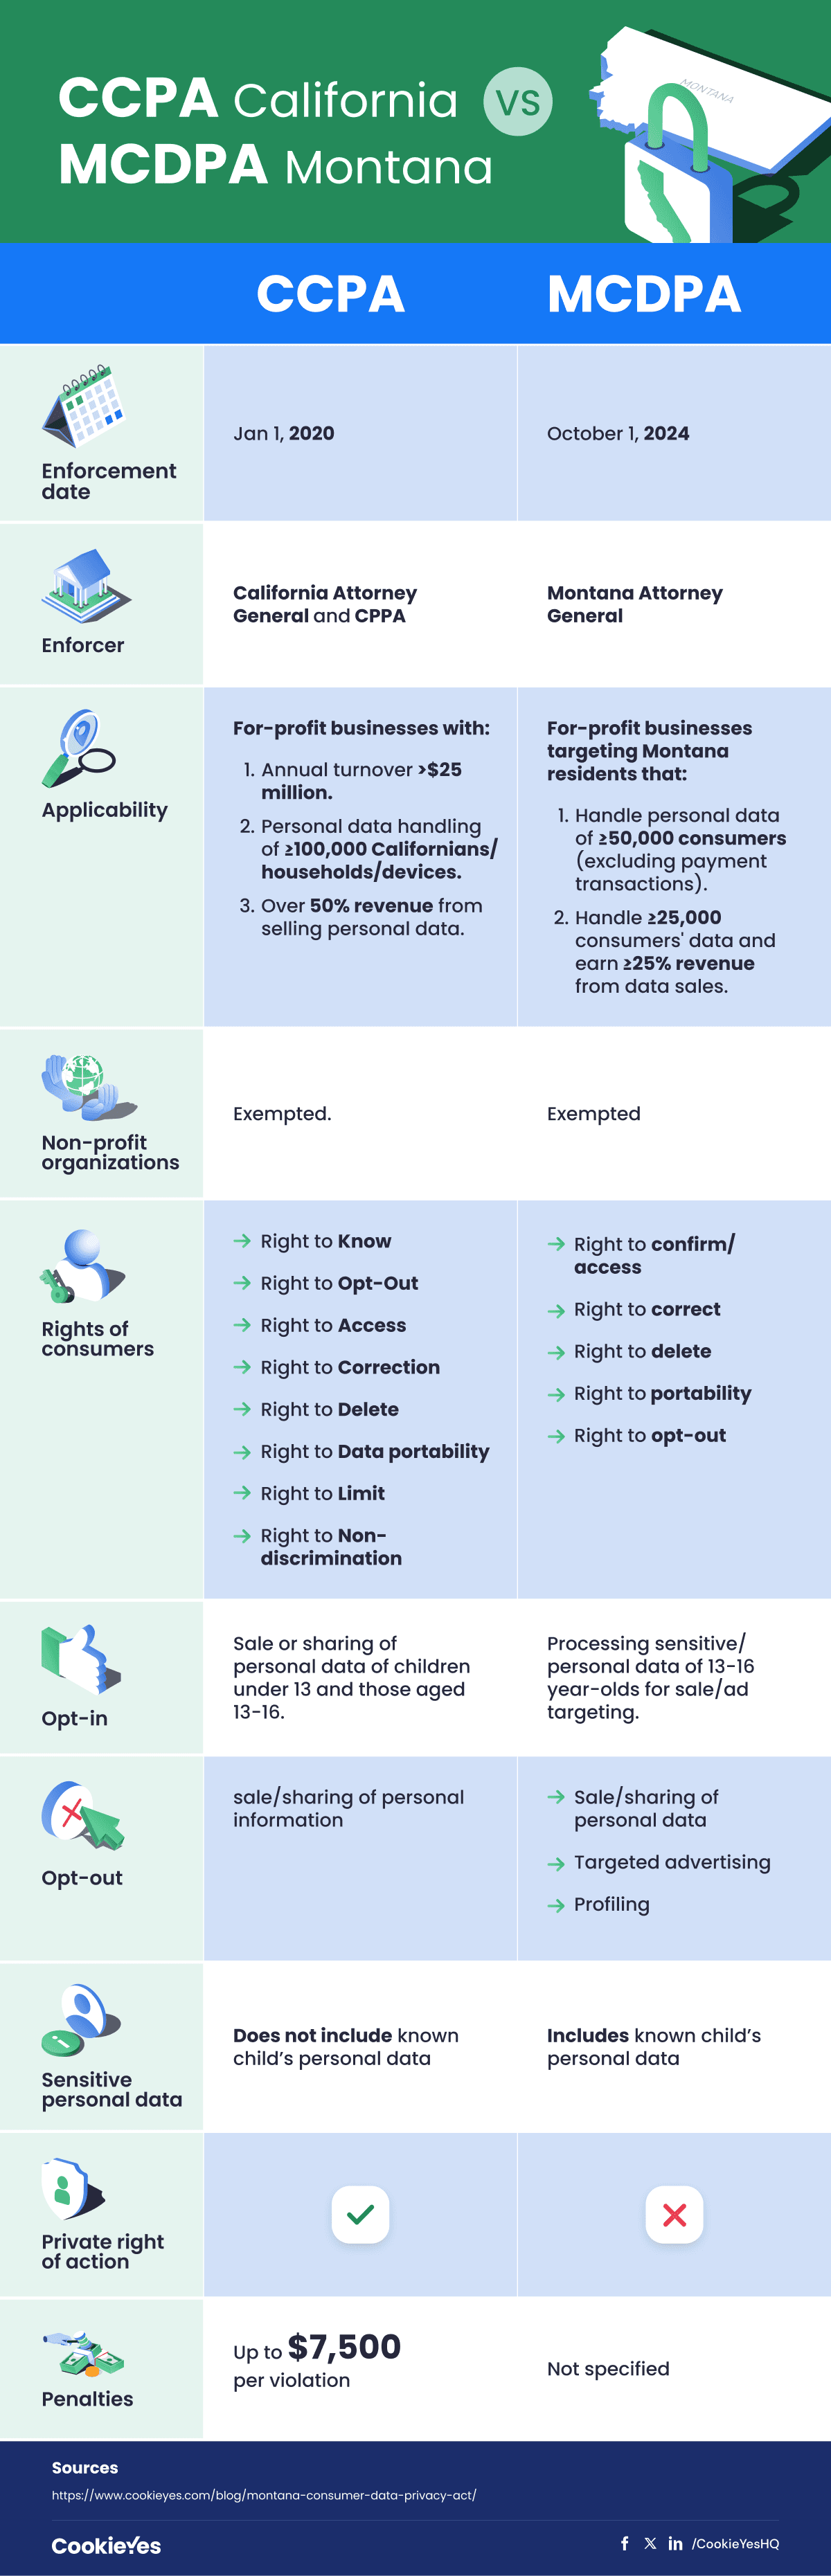
CCPA vs MCDPA [Infographic]
Checklist for MCDPA compliance
- Collect only the personal data necessary for disclosed purposes.
- Limit the processing to what is required to fulfill the specific purpose.
- Obtain consent to process sensitive data.
- Follow the additional consent and safety requirements for minors under 18.
- Provide a convenient consent withdrawal mechanism.
- Publish a clear, accessible and up-to-date privacy notice.
- Implement security safeguards.
- Provide opt-out mechanisms.
- Recognize global opt-out signals.
- Do not discriminate among consumers based on the exercise of rights.
- Create and implement a response plan for consumer requests.
- Have a contractual relationship with processors.
- Conduct regular data protection assessments.
FAQ on Montana Consumer Data Privacy Act
Does Montana have a privacy law?
Yes. Montana's Consumer Data Privacy Act (MCDPA) took effect on 1 October 2024. It was amended by SB 297, which took effect on 1 October 2025 and introduced broader coverage, stronger protections for minors and additional compliance requirements.
What is the penalty for the Montana Consumer Data Privacy Act?
Violations of the MCDPA can result in civil penalties of up to $7,500 per violation. The Montana Attorney General has exclusive enforcement authority and may also seek injunctive relief and recover reasonable enforcement costs.
What constitutes the sale of personal data under MCDPA?
Exchange of personal data to third parties for monetary or any other valuable consideration constitutes a sale.
Is there a cure period under MCDPA?
No. SB 297 removed the law's previous mandatory 60-day cure period. Businesses should not assume they will receive an opportunity to correct a violation before enforcement action.