Full site index for AI agents: llms.txt. Every page is also available as Markdown: replace the trailing slash with .md, so /pricing/ becomes /pricing.md. Or send the header Accept: text/markdown to the page URL itself.
Meet the CookieYes Claude MCP Server. Bringing cookie compliance workflows directly into Claude.
Compliance with the General Data Protection Regulation requires more than just good intentions; it demands proper documentation. Stay on the right side of the EU data privacy law with this ultimate list of key GDPR documents for compliance.
Why GDPR documentation is crucial for compliance?
The GDPR aims to protect individual privacy and uphold the lawful, transparent, and secure processing of personal data.
Businesses operating in EEA/EU member states or those handling EU personal data must match their data processing activities with GDPR standards. This also means maintaining accurate and up-to-date records to prove compliance with the law.
However, GDPR documentation is more than just a legal requirement; it serves as a framework for regulating data processing operations as well as a tool for demonstrating compliance to authorities and stakeholders.
Key GDPR documents include records of Data Protection Impact Assessments (DPIAs), privacy notices, and data protection and retention policies.
The top reasons that make GDPR documentation crucial include:
Demonstrating compliance
The accountability principle and Article 24 of GDPR mandate that businesses demonstrate compliance with the law, including the data protection principles. GDPR documentation helps businesses meet this requirement.
Record-keeping obligation
Article 30 of the GDPR necessitates data controllers and processors to maintain records of their data processing operations and to cooperate with supervisory/data protection authorities by making the records available when requested.
Preparation for emerging technologies
As businesses adopt AI and automation, GDPR documentation becomes increasingly crucial. Often, these processes require collecting and handling personal data, necessitating close monitoring for GDPR compliance.
This includes the records of processing activities, Data Protection Impact Assessments, categories of personal data collected, and purposes of the processing.
Avoid legal consequences
Organisations caught in violation of GDPR obligations can face serious fines of up to 20 million euros or 4 per cent of their annual revenue.
10 essential GDPR documents for your business
Below is a list of documents essential for compliance with EU data protection law.
#1 Privacy policy
Under GDPR, Article 12 outlines transparency requirements, Article 13 specifies disclosure obligations for direct data collection and Article 14 covers disclosure for indirect data collection. These articles collectively emphasise the importance of transparency in data practices.
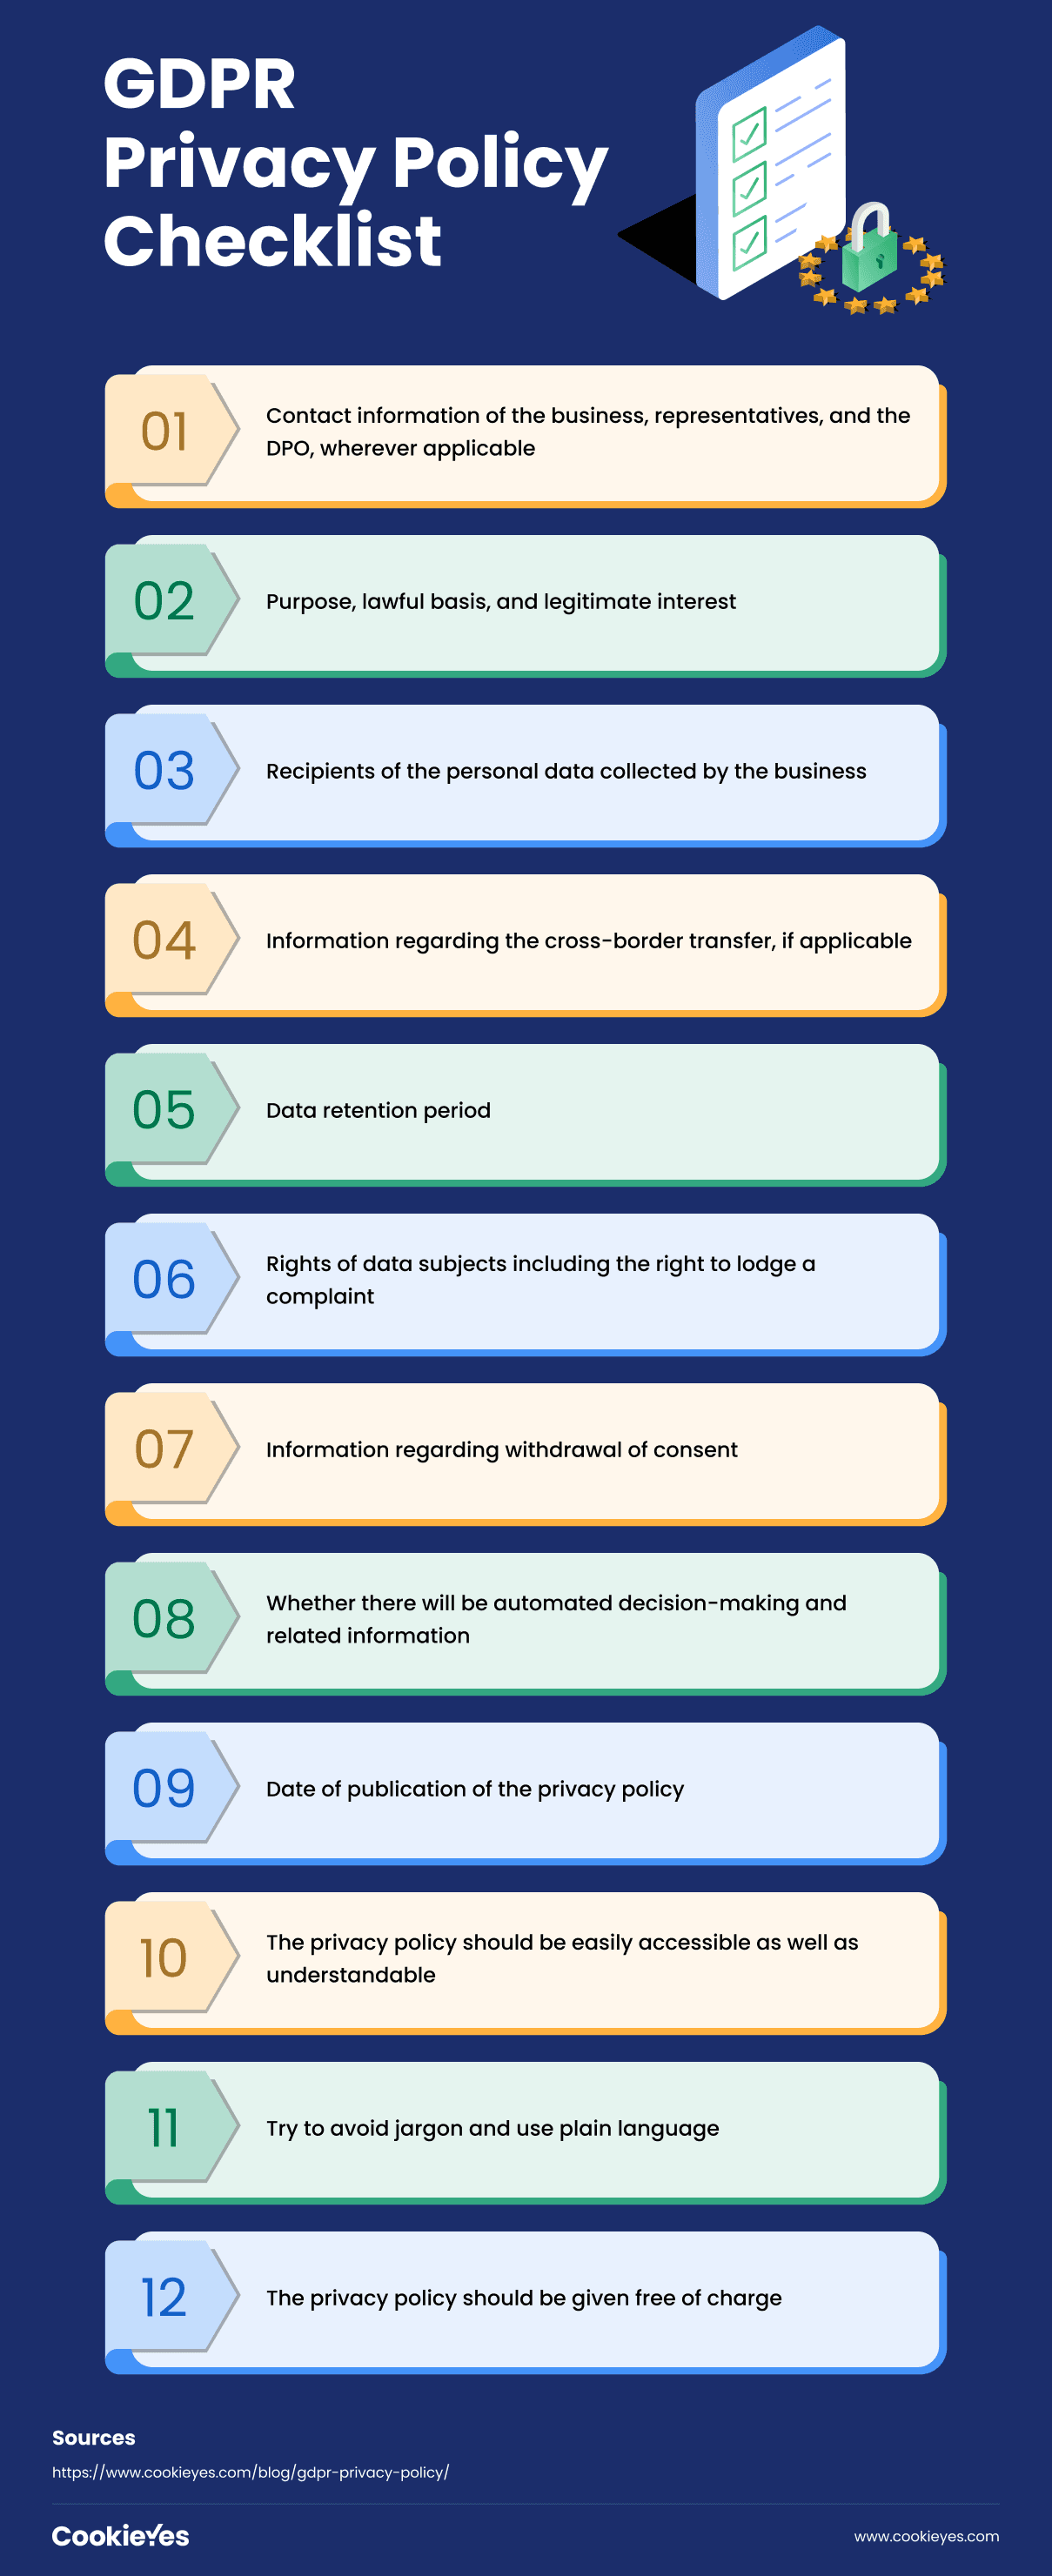
A privacy policy/privacy notice tells data subjects what personal data an organisation collects, why they need it, how they will be used, and how they keep it safe.
It should typically include:
Name and contact information of the organisation
Categories of personal data collected and their sources
Data storage period
Specific purposes/ legal bases/legitimate interests for processing
Data sharing specifics including international transfers
Data subject rights such as the right of access, erasure, rectification, data portability
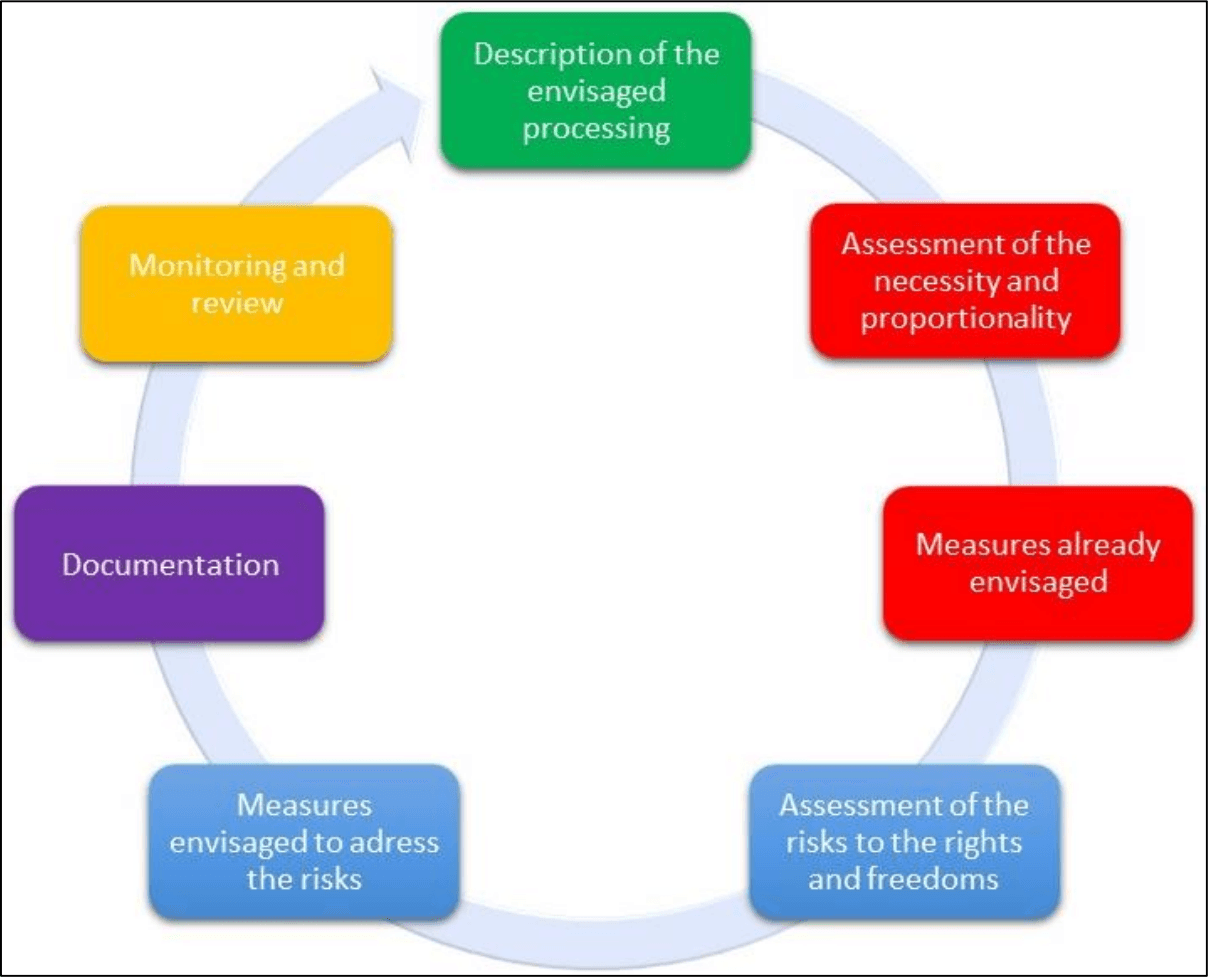
A privacy assessment register is a structured document that contains information about all the DPIAs conducted by your organisation. They are mostly carried out to assess the impacts of data processing activities on high-risk data like sensitive information.
Data Protection Working Party guidelines on the process for carrying out DPIAs
A DPIA register typically contains:
A detailed and specific description of data processing operations including the types of personal data processed and the retention period
Assessment of the necessity and proportionality of the processing in relation to legal bases, legitimate interests and data subject rights
Analysis of any risks to the rights and freedom of individuals
Advises or comments from concerned parties such as the Data Protection Officer (DPO) or individuals
#3 Data protection policy
A data protection policy is like a route map for employees to aid GDPR implementation in daily operations. It clearly defines the rules for collecting, processing, storing, deleting and protecting personal data. The policy also brings consistency to the operations within the organisation.
It usually includes:
An introduction that sets the objective and scope of the policy
Definition of the critical terms outlined in the policy
The extent of the GDPR's application
Data protection principles and your organisation’s adherence to it
The GDPR requirements for privacy-compliant data processing
Roles and responsibilities of stakeholders like employees, DPO and third-party processors
Explanation of the data subject rights and guidelines for handling requests
Guidelines on data processing practices including collection and retention of personal data
Data protection measures implemented
Information about the awareness training programmes for employees
#4 Data Processing Agreement
GDPR’s Article 28 (3) requires businesses to have a contractual relationship with their processors. A DPA is a legal agreement between a data controller and a data processor that specifies the terms and conditions for processing personal data by a third-party service on behalf of the data controller.
A DPA must cover:
The definition of key terms in the agreement
Roles and responsibilities of each party
Details and duration of data processing activities
Purpose of processing
Subject matter of the agreement (Categories of personal data)
Technical and organisational measures implemented by the parties
Audit rights to the controller
Instructions on deletion and return of personal data
#5 Records of Processing Activities (RoPA)
The RoPA is a document that demonstrates compliance with the data processing requirements of GDPR. Controllers and processors with 250+ employees must record all operations involving personal data that fall under their responsibility.
Article 30 of GDPR prescribes the following information to be included in an organisation's RoPA:
Name and contact details of the organisation
Categories and purpose of processing
Categories of data subjects involved in the processing
Recipients of the data
Data retention period
General description of the data security safeguards implemented
#6 Consent forms
GDPR sets out strict consent rules for businesses processing EU personal data.
GDPR consent must be a free, informed, unambiguous, and specific affirmative act of the data subject indicating their willingness to allow data processing.
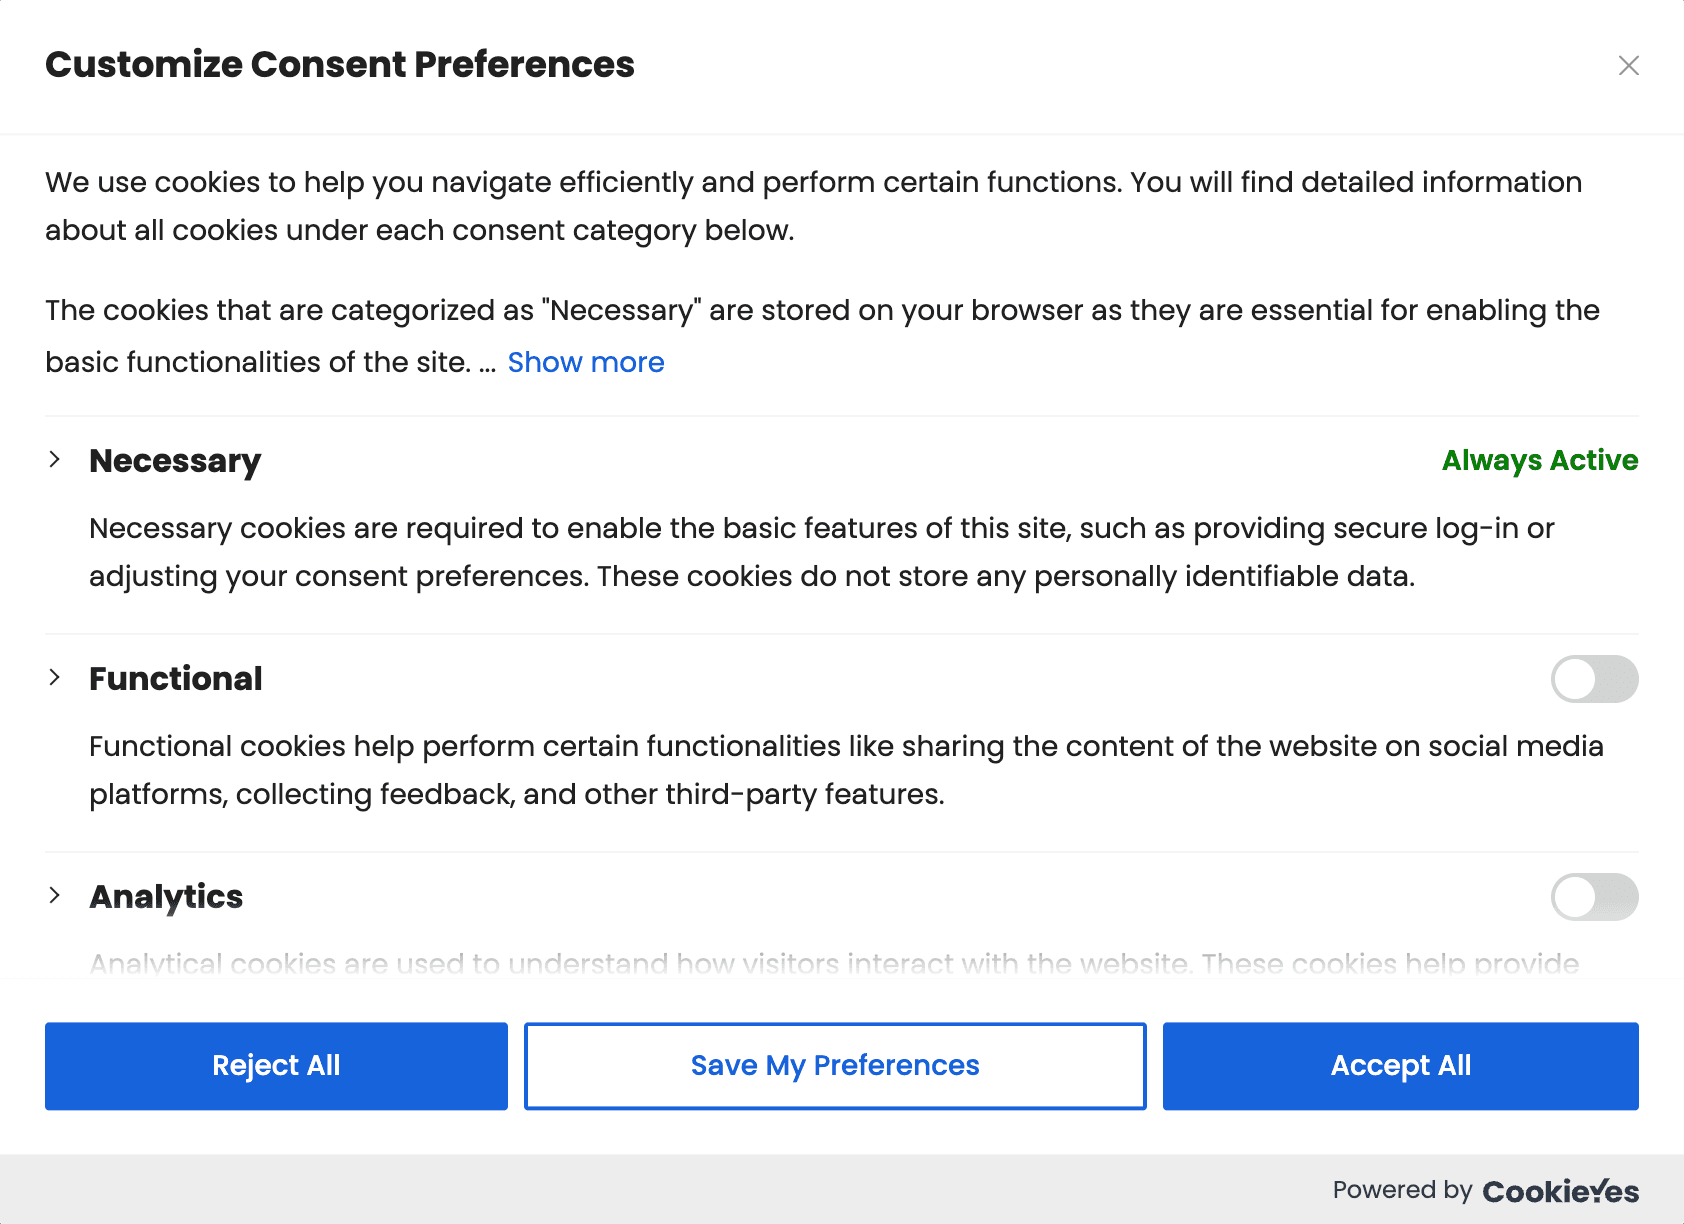
A consent form should be concise, conspicuous and free from any jargon.
Cookie consent form powered by CookieYes
It must at least include:
Name of the organisation
Specific purposes and a brief description of the processing
Withdrawal mechanism
Link to a detailed privacy statement
Opt-in mechanisms like a tickbox, toggle buttons or a signature block
Take the first step to GDPR compliance
Easily create a cookie banner and ensure your GDPR compliance today
A data breach response plan is a comprehensive document that outlines the steps employees must follow in the event of a personal data breach. It guides them in identifying, reporting and containing breaches.
The document also includes a pre-prepared notification template to be given to the supervisory authorities and affected individuals ensuring compliance with the data breach notification obligations under the law.
The key elements of a breach response plan are:
The process to identify, assess the impact and mitigate the breach promptly
Internal reporting guidelines
Guidelines on when and how to report the breach to supervisory authorities and affected data subjects
Notification templates
Actions to contain and reduce the impact of the breach
Roles of employees in the event of a breach
#8 Data breach register
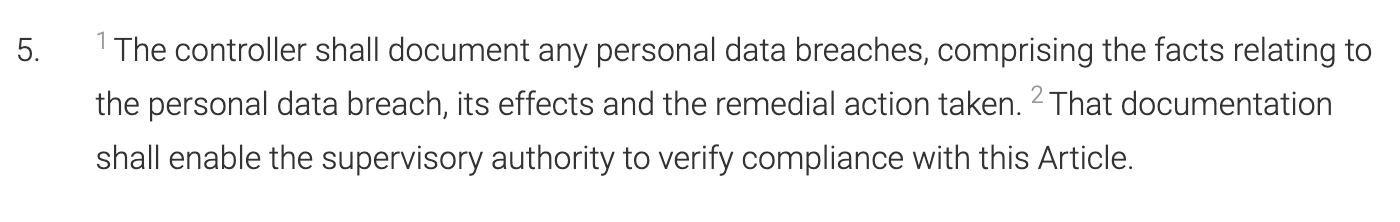
Article 33 (5) of GDPR requires all controllers to maintain a breach register comprising the information related to the personal data breach, the impacts caused and the actions the organisation has taken to mitigate it.
Article 33(5) of GDPR
#9 Data retention policy
The storage limitation principle and associated GDPR obligations restrict the indefinite storage of personal data. To comply with the law, businesses must have a data retention policy that sets the criteria for how long specific categories of data should be stored.
A data retention policy must at least include:
Types of information covered by the policy
Specify the duration for which it will be retained or the criteria for determining the duration
Exceptions to the storage limitation if there are any
Actions to be taken after the retention period
#10 Standard Contractual Clauses or Binding Corporate Rules
SCC and BCR are legal arrangements enabling cross-border data transfers.
Standard Contractual Clauses are legal agreements approved by the European Commission allowing businesses to transfer personal data outside the European Union or the European Economic Area.
Binding Corporate Rules, on the other hand, are internal policies adopted by multinational corporations, especially, to enable data transfer to entities or branches that are not EEA or European members.
Effective tips for maintaining GDPR documents
Maintaining your GDPR documents ensures your organisation’s compliance over time. Here are a few key practices to help you achieve it.
Regular updates
GDPR documentation requires an ongoing and proactive effort. Therefore, review and update your GDPR documents regularly.
Centralise documentation storage
Implementing a document management system along with centralised storage for files guarantees that all stakeholders can easily access the most recent versions of all essential documents.
Implement version controls and change logs
Establish a version control system that records all changes made to the document. This helps you track the version history and maintain a clear audit trail for regulatory reviews.
Train employees
Hold consistent training sessions to ensure your staff understands and follows GDPR guidelines when managing personal information.
Conduct internal audits
Regular audits should be conducted to ascertain whether the GDPR documents are being implemented correctly within the organisation.
Appoint a DPO
You may also appoint a data protection officer to oversee the implementation of GDPR, especially if handling large amounts of personal or special categories of data.
FAQ on GDPR documents
What is GDPR and why are GDPR documents important?
GDPR is the European data protection law that controls how organisations handle the personal data of EU residents. GDPR documents are important as they serve as a framework for demonstrating compliance, managing data and avoiding GDPR fines.
Do small businesses also need GDPR documents?
Yes, GDPR is applicable to all businesses, including small ones. While there are a few exceptions such as for records of processing activities, most small businesses are still required to maintain relevant GDPR documents.
Can businesses use templates for GDPR documents or do they need custom legal advice?
Templates can be a starting point for businesses. However, GDPR requires customisation based on the type of business, processing activities, and business operations. Therefore, it is advisable to seek legal advice to ensure that your documents align with GDPR requirements.
How does a privacy policy differ from a cookie policy?
A privacy policy is a detailed document describing the data handling practices of an organisation including how it collects, stores, processes or shares personal data. Whereas, a cookie policy explains the use of cookies on a website such as the types of cookies, their purposes, and how users can manage cookie preferences. For more guidance, check out cookie policy examples and templates.
How often should GDPR documents be reviewed and updated?
GDPR documents should be updated and reviewed regularly, at least once a year or whenever there are significant changes to your business processes, legal requirements or technology.